Delivery · code quality
Reviews every pull request: security, performance, style. Leaves concrete line-level comments and guards the team's standards.
- Input
- a pull request
- Output
- a review with line comments
- Scope
- security · performance · style

What it does
Scope of work
A review for every PR
Security, performance, readability and team standards - on every pull request, not just when someone has time.
Quality · every PR
Line-level comments
A concrete problem, a concrete line, a suggested fix. No vague “looks good to me”.
Precision · line-level
Guards the standards
Repo conventions, architecture patterns and team checklists are part of its context - enforced consistently for people and agents alike.
Standards · team consistency
In the product
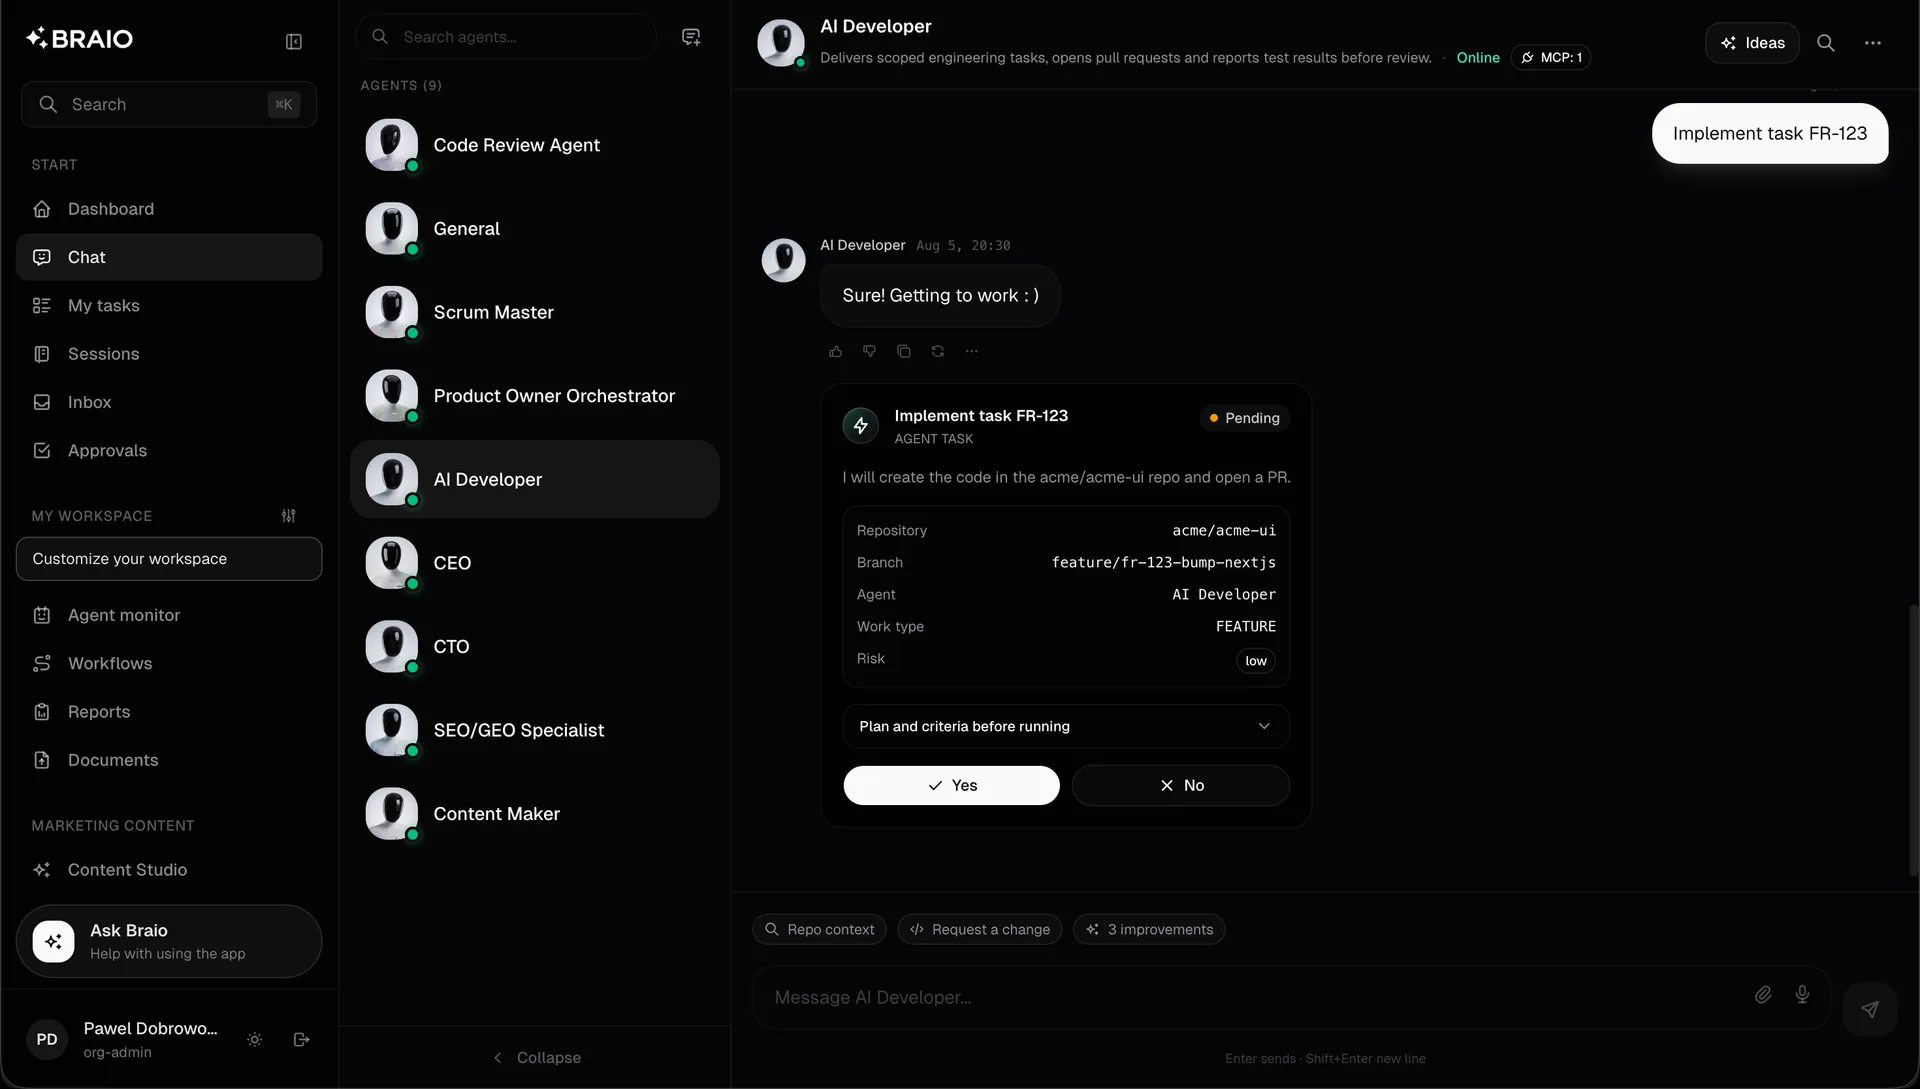
This is what it looks like in Braio
- Verification is a separate loop step - code is checked by a different agent than the one that wrote it
- Line comments in GitHub / GitLab
- Review results included in the evidence report
How it works
One loop, six steps
- 01Taskfrom chat, backlog or a schedule
- 02Plan & criteriaexplicit scope, repo, branch, risk level
- 03Your approvala Yes/No gate before anything runs
- 04Executioncode, content or analysis in your tools
- 05Verificationcode review, tests, in-browser QA
- 06Evidence reportscreenshots, timeline, metrics
Approval gate: the review happens automatically; the merge decision always belongs to a human or to rules you set yourself.
Control
Autonomy on your terms
The review itself is level 1 - comments plus an audit log entry. Approve-with-auto-merge can only be enabled as level 2, with an SLA timer and a rollback plan.
Scenario · Software house
- Today
- code review blocks sprints and depends on a senior's availability
- With Braio
- every PR gets a review in minutes, and the senior looks only where the agent flags risk